Vahid Ismayilov
DevSecOps & Application Security Engineer
Hi, I'm Vahid Ismayilov — a DevSecOps and Application Security Engineer focused on building secure software delivery pipelines, improving application security, and reducing security risks across modern cloud-native environments.
My work sits at the intersection of DevSecOps, Application Security (AppSec), Cloud-Native Security, and AI Security. I believe effective security is not just about finding vulnerabilities; it is about understanding their real-world impact, prioritizing exploitable risks, and integrating security into engineering workflows without unnecessarily slowing down development.
Interdisciplinary Technical Focus
Modern security requires bridging developer velocity, infrastructure hardening, risk correlation, and artificial intelligence safety.
DevSecOps & CI/CD
Embedding automated security gates, policy-as-code, and continuous vulnerability verification directly into development workflows.
Application Security
SAST, DAST, SCA, API security reviews, and developer enablement to eliminate architectural weaknesses at the root.
Cloud-Native & K8s
Applying verified CKS-level controls, admission governance, container isolation, and immutable infrastructure defense.
ASPM & AI Security
Correlating multi-scanner telemetry to prioritize real exploitable attack chains and securing modern AI-enabled systems.
Evidence-Based Security & ASPM Lifecycle
A cohesive engineering pipeline moving from architectural threat modeling to continuous, reachability-verified vulnerability triage.
ASPM & Risk Correlation — Evidence-Based Triage
Correlating multi-source scanner signals to eliminate noise, verify reachability, and map genuine attack chains rather than chasing raw alert counts.
Detailed Technical Focus Areas
Hands-on technical capabilities applied across application security tooling, pipeline automation, and cloud-native workloads.
Application Security (AppSec)
SAST, DAST, SCA, OWASP Top 10, API security, vulnerability analysis, and secure SDLC practices.
- SAST & DAST orchestration
- SCA & dependency analysis
- OWASP Top 10 mitigation
- API security & schema validation
- Secure code reviews & SDLC
DevSecOps & Security Automation
CI/CD security gates, automated security testing, vulnerability management, and security policy enforcement.
- Automated CI/CD security gates
- Policy-as-Code enforcement
- Automated vulnerability workflows
- Security toolchain integration
- Developer-friendly feedback loops
Cloud-Native Security
Kubernetes, container security, infrastructure security, and cloud-native workload protection.
- Kubernetes hardening (CKS/CKA)
- Container image signing & scanning
- Pod security standards & admission
- Network policies & RBAC auditing
- Cloud workload posture defense
ASPM & Risk-Based Security
Security finding correlation, false-positive reduction, exploitability analysis, attack-chain reasoning, and risk prioritization.
- Cross-scanner finding correlation
- False-positive filtering algorithms
- Exploitability & reachability analysis
- Attack-chain reasoning & graph modeling
- Evidence-based risk scoring
Software Supply Chain Security
SBOM generation, dependency risk analysis, and software supply chain visibility.
- Automated SBOM generation (SPDX/CycloneDX)
- Transitive dependency risk scoring
- Vulnerability telemetry tracking
- Secrets detection & leak prevention
- Supply chain integrity controls
AI Security
LLM security, prompt injection, AI threat modeling, model security assessment, and emerging security challenges in AI-enabled systems.
- LLM threat modeling & OWASP Top 10 for LLMs
- Prompt injection & jailbreak defense
- AI model security assessment
- Certified AI Security Professional (CAISP)
- Secure AI agent integration patterns
Professional Certifications
Hands-on technical credentials validated through rigorous official examinations across AI security, Kubernetes architecture, and application defense.
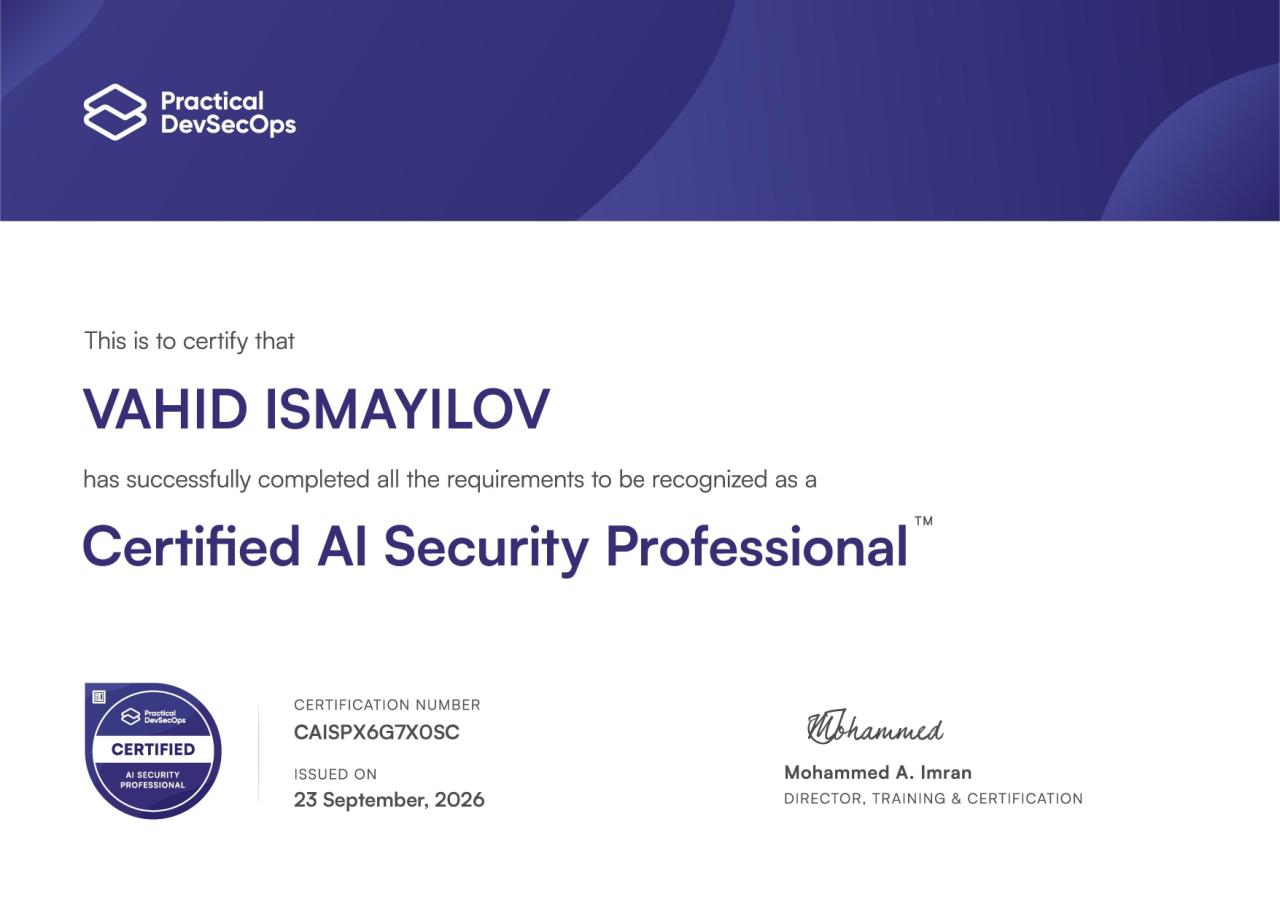
CAISP — Certified Artificial Intelligence Security Professional
Covers AI security concepts, LLM threats, prompt injection, adversarial machine learning, model security, and AI supply chain security, in line with the official syllabus.
Engineering-First Security
Moving beyond alert-driven fatigue to evidence-based defense
Root-Cause Engineering
Identify the underlying architectural weakness, understand the attack path, validate reproducible evidence, and help engineering teams implement practical remediation at the code level.
Evidence-Based Risk Prioritization
Move beyond alert-driven security toward contextualized, evidence-based engineering. High alert volumes without reachability analysis cause friction; contextual telemetry drives decisive action.
Open Knowledge Sharing & Research
This platform is where technical investigations, hands-on labs, vulnerability analyses, security tooling experiments, and lessons learned across DevSecOps, AppSec, Kubernetes, and AI security are documented openly.
"My long-term goal is to grow into a Principal Security Engineer role, combining deep technical expertise with security architecture, automation, and engineering leadership."
Explore my work, follow my experiments, and let's build more secure systems.
Have an AppSec or DevSecOps inquiry?
Feel free to reach out for technical discussions, vulnerability remediation guidance, or security architecture reviews.
[email protected]